hackers
Microsoft says threat actors are ahead in the early AI race
Microsoft says cyberattackers are currently benefiting from artificial intelligence faster than defenders, allowing threat actors to speed up vulnerability discovery, malware development, and post-compromise activity while security teams struggle to keep pace. This comes from Microsoft’s 2026 Digital Defense Report, which strongly focuses on how artificial intelligence is changing both offensive and defensive cybersecurity operations. […]
Australia arrests alleged TeamPCP hackers behind supply-chain attacks
Australian authorities have arrested and charged two young men accused of being part of the TeamPCP hacking group linked to a string of far-reaching developer supply chain attacks. TeamPCP is a hacking group known for widespread supply-chain attacks over the past year that targeted open-source software and developer platforms to steal credentials, authentication secrets, and […]
New BlackFile extortion group linked to surge of vishing attacks
A new financially motivated hacking group tracked as BlackFile has been linked to a wave of data theft and extortion attacks against retail and hospitality organizations since February 2026. The group, also tracked as CL-CRI-1116, UNC6671, and Cordial Spider, is impersonating corporate IT helpdesk staff to steal employee credentials and demand seven-figure ransoms, according to information shared […]
UK warns of Chinese hackers using proxy networks to evade detection
The United Kingdom’s National Cyber Security Centre (NCSC-UK) and international partners warned that China-nexus hackers are increasingly using large-scale proxy networks of hijacked consumer devices to evade detection and disguise their malicious activity. This joint advisory, co-signed by agencies from the United States, Australia, Canada, Germany, Japan, the Netherlands, New Zealand, Spain, and Sweden, says […]
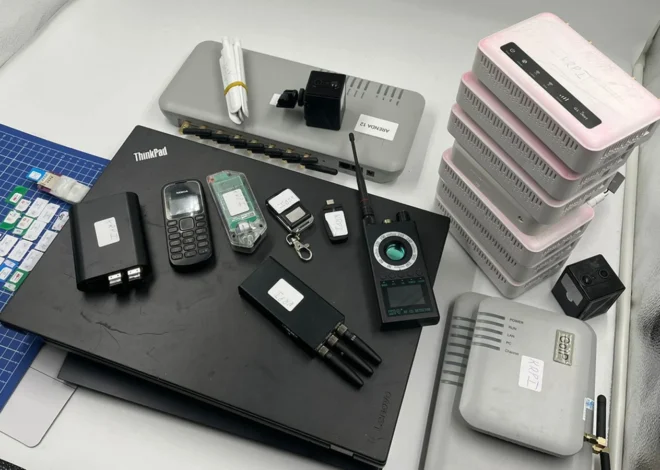
Poland arrests Ukrainians utilizing ‘advanced’ hacking equipment
The police in Poland arrested three Ukrainian nationals for allegedly attempting to damage IT systems in the country using hacking equipment and for obtaining “computer data of particular importance to national defense.” The three men, aged between 39 and 43, could not explain why they were carrying the electronic devices. They now face charges of fraud, computer […]
Portugal updates cybercrime law to exempt security researchers
Portugal has modified its cybercrime law to establish a legal safe harbor for good-faith security research and to make hacking non-punishable under certain strict conditions. First spotted by Daniel Cuthbert, a new provision in Article 8.o-A, titled “Acts not punishable due to public interest in cybersecurity,” provides a legal exemption for actions that previously were classified as illegal system […]

Hackers ramp up scans for leaked Git tokens and secrets
Threat actors are intensifying internet-wide scanning for Git configuration files that can reveal sensitive secrets and authentication tokens used to compromise cloud services and source code repositories. In a new report from threat monitoring firm GreyNoise, researchers have recorded a massive spike in searches for exposed Git configs between April 20-21, 2025. “GreyNoise observed nearly […]
Hackers lurked in Treasury OCC’s systems since June 2023 breach
Unknown hackers who breached the Treasury’s Office of the Comptroller of the Currency (OCC) in June 2023 gained access to over 150,000 emails, according to anonymous sources familiar with the matter. The OCC is an independent bureau of the U.S. Department of the Treasury that oversees banks and federal savings associations and ensures they comply […]
North Korean hackers linked to $1.5 billion ByBit crypto heist
Over the weekend, blockchain security companies and experts have linked North Korea’s Lazarus hacking group to the theft of over $1.5 billion from cryptocurrency exchange Bybit. In what is now considered the largest crypto heist in history, the attackers intercepted a planned transfer of funds from one of Bybit’s cold wallets into a hot wallet, […]
Hackers exploit critical unpatched flaw in Zyxel CPE devices
Hackers are exploiting a critical command injection vulnerability in Zyxel CPE Series devices that is currently tracked as CVE-2024-40891 and remains unpatched since last July. The vulnerability allows unauthenticated attackers to execute arbitrary commands using the ‘supervisor’ or ‘zyuser’ service accounts. Vulnerability intelligence company VulnCheck added the security issue to its database last year on July 12 and […]