cybersecurity

OpenAI’s GPT-6.1 Terra is safer overall, but shows more destructive-action flags in tests
OpenAI confirmed GPT-6.1 Terra is safer overall than some of its older models, but its safety testing also found other problems. According to OpenAI, GPT-6.1 Terra showed higher rates of exfiltration, destructive actions, and attempts to bypass restrictions than GPT-6.1 Sol and GPT-6 Astra. OpenAI performed simulations across approximately 48,690 matched tasks and found that […]
Hackers breach Microsoft 365 tenants via ConnectWise supply-chain attack
ConnectWise has shut down customer access to its Cloud Backup service (formerly SkyKick Cloud Backup) after hackers accessed application identities and compromised Microsoft 365 tenants. Reports of the malicious activity began emerging on Friday, with administrators observing unauthorized access to client data in Microsoft 365 tenants due to a potential “SkyKick/CW breach.” Later on the […]
South Korea probes bank breaches amid suspected AI-powered attacks
South Korea’s Financial Services Commission (FSC) held an emergency meeting following a series of cyberattacks targeting financial institutions in the country. During the meeting, officials confirmed a data breach at Shinhan Bank and said other cybersecurity incidents affected other South Korean banks, including Kookmin Bank. Shinhan Bank and KB Kookmin Bank are large private South […]
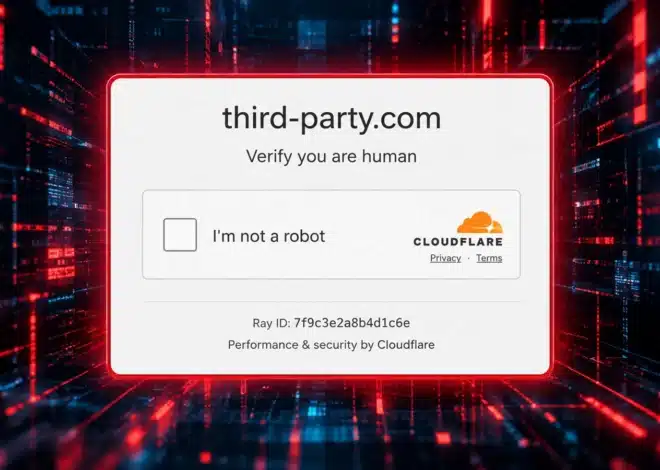
Placeholder domain used in dev docs now serves ClickFix attacks
The “third-party.com” domain, commonly used as a placeholder in developer documentation and code examples, is serving a fake Cloudflare verification page that attempts to trick Windows users into executing PowerShell commands. The domain third-party.com has long been used in documentation to represent an arbitrary external website, API, or service, similar to how developers use domains such […]
InfraTrust report warns network management systems under attack
Attackers are increasingly targeting the management systems used to control enterprise infrastructure, with several critical vulnerabilities actively exploited before or shortly after vendors disclosed them. This was reported in the September edition of Eclypsium’s InfraTrust Pulse, a monthly report tracking security advisories affecting network devices, servers, firmware, chips, and other infrastructure. Between August 25 and […]
Rogue external MFA providers can steal passwords during logins
Security researchers developed an attack that lets hackers with privileged access register a rogue external MFA provider that steals users’ passwords during legitimate login attempts. The technique, dubbed TrustSink by Varonis Threat Labs, can work with any provider that relies on this external authentication model, though the researchers demonstrated the attack using Microsoft Entra. Microsoft […]
Microsoft adds age-awareness APIs that can tell if users are children, teens, or adults
Microsoft is adding new age-awareness APIs to Windows 11 that will allow apps to determine whether someone is a child, teenager, or adult without exposing their exact date of birth. The new Windows Age API uses information associated with a Microsoft account and can return age ranges such as under 10, 10-12, 13-15, 16-17, and […]

Apple sends new ‘Threat Notification’ alerts over mercenary spyware attacks
You’re not alone if you just received an “Apple Threat Notification” saying it detected a “mercenary spyware attack targeted at your iPhone.” Apple confirmed to GeekFeed that it sent a new batch of threat notifications on August 13 to targeted users in 110 countries. Some users on Reddit also reported receiving the alerts, but the feature itself […]

White House taps security firms for offensive hack-back operations
A new White House memo signed by U.S. President Donald Trump instructs the National Coordination Center (NCC) to establish a program that would allow private security companies to apply for approval to hack foreign cybercrime organizations. Signed on Wednesday, the national security presidential memorandum (NSPM) enables the NCC (part of the Homeland Security Task Force) […]