Hardware
Dive into the dynamic world of technology with our Hardware category. Stay updated with the latest advancements, reviews, and in-depth analyses of computer components, peripherals, and essential tech gadgets. From cutting-edge innovations to detailed product insights, our coverage ensures you’re equipped with the knowledge to make informed decisions and stay ahead in the ever-evolving hardware landscape.
Trezor warns of suspected crypto-theft implant in hardware wallet
Hardware wallet device maker Trezor has received credible reports about a suspected hardware crypto-theft implant in a Trezor Safe 5 sold by its reseller CryptoBilis in Southeast Asia. Although the company has not yet received the device to examine it and confirm whether there is a malicious implant, it has warned potentially affected users to […]
Ledger asks sellers across Asia to halt sales after supply-chain attack
Ledger is asking resellers and distributors in Southeast Asia and Hong Kong to halt wallet sales and remove products from shelves while it investigates hardware implant incidents. The company announced the decision in response to discovering that devices purchased from CryptoBilis had been modified to steal seed phrases used to access crypto assets and send […]
New Spectre v2 attack variant leaks Linux root password hash in minutes
A new Spectre v2 attack variant called Branch Target Reuse (BTR) can recover root password hashes from Intel computers running Linux in just a few minutes. A BTR attack exploits stale information in a processor’s branch predictor after a just-in-time (JIT) engine reuses memory for new code. By manipulating this leftover information, an attacker can […]

Hackers exploit new MikroTik RouterOS flaws to hijack routers
Hackers are exploiting a chain of two recently disclosed vulnerabilities in MikroTik routers to take control of devices with SSH services exposed to the internet. One of the security issues, tracked as CVE-2026-67276, is an SSH authentication bypass flaw in MikroTik RouterOS caused by incomplete validation of RSA public keys. An attacker who knows a […]
Hackers infect Android car head units with proxy botnet malware
A supply-chain attack targeting Android-based car head units is using a legitimate device-update app to spread malware that enlists compromised devices in a proxy botnet or uses them for ad fraud. Kaspersky researchers analyzed the malware and attributed the operation to the MoYu group, a threat actor previously associated with the BadBox malware botnet. The researchers […]

Hackers compromise 14,500 Dahua web cameras in 35-day campaign
In a large-scale campaign that researchers dubbed CameraSwarm, hackers compromised more than 14,500 Dahua IP cameras mostly in Ukraine and Russia. The operation ran for at least 35 days between June 17 and July 22, compromising devices by exploiting vulnerabilities, brute-forcing logins, and using offline recovery codes from serial numbers for cloud-registered cameras. Researchers at threat […]
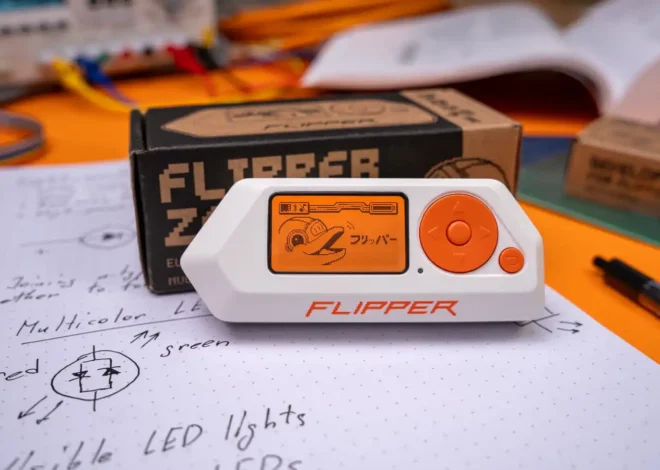
Flipper Zero firmware development continues with community help
Flipper Devices says development of the Flipper Zero firmware will continue, albeit with a smaller internal team and greater reliance on community contributions. The announcement comes as the gadget maker decided to focus on building new devices, like the Flipper One open Linux platform, for which the company turned to the community’s help to complete development. There […]
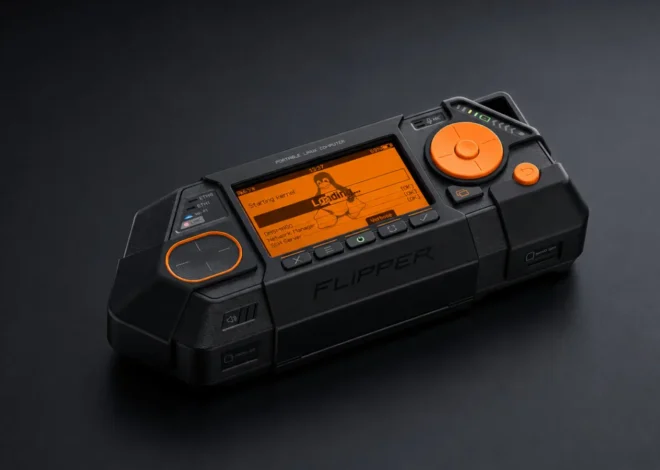
Flipper One project needs community help to build open Linux platform
Flipper Devices, the maker of the Flipper Zero pentesting tool, is asking the community to help build Flipper One, an open Linux platform for connected devices. Unlike Flipper Zero, which focuses on offline access control and radio technologies such as NFC, RFID, infrared, and sub-GHz communications, the Flipper One project is designed as a high-performance, Linux-based […]
New Mirai campaign exploits RCE flaw in EoL D-Link routers
A new Mirai-based malware campaign is actively exploiting CVE-2025-29635, a high-severity command-injection vulnerability affecting D-Link DIR-823X routers, to enlist devices into the botnet. CVE-2025-29635 allows an attacker to execute arbitrary commands on remote devices by sending a POST request to a vulnerable endpoint, triggering remote command execution (RCE). Akamai’s SIRT, which detected the Mirai campaign in March […]
New GPUBreach attack enables system takeover via GPU rowhammer
A new attack, dubbed GPUBreach, can induce Rowhammer bit-flips on GPU GDDR6 memories to escalate privileges and lead to a full system compromise. GPUBreach was developed by a team of researchers at the University of Toronto, and full details will be presented at the upcoming IEEE Symposium on Security & Privacy on April 13 in […]