Zero-Day
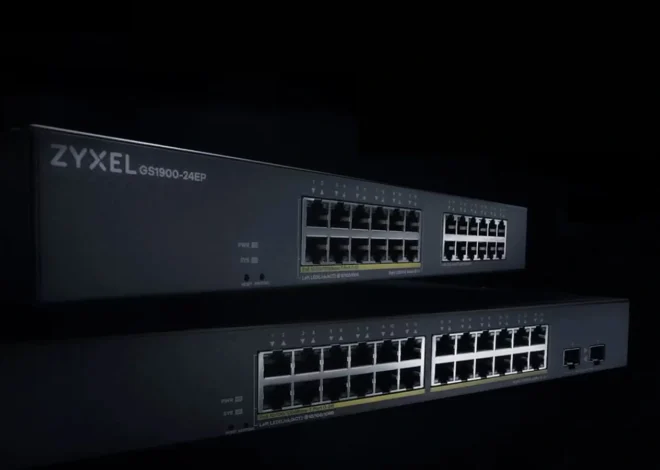
Zyxel fixes zero-day exploited to hack nearly 1,000 network switches
Zyxel has patched a zero-day vulnerability in its GS1900 series network switches that hackers exploited to compromise nearly 1,000 devices worldwide and steal configuration files and credentials. The vulnerability, tracked as CVE-2026-107441, is an out-of-bounds write flaw in the switches’ web management interface that allows an unauthenticated attacker with network access to execute operating system […]
Ivanti patches two more Connect Secure zero-days chained in attacks
Ivanti released security updates to patch two more Connect Secure (ICS) remote access gateway flaws that have been chained in zero-day attacks since at least October 1. Threat actors exploited these two flaws (tracked as CVE-2026-111357 and CVE-2026-118527) alongside an authentication bypass vulnerability (CVE-2026-104935), which Ivanti patched last month to remove the main attack surface. CVE-2026-111357 is a high-severity privilege […]

New Cisco firewall zero-day exploited to crash SSL VPN devices
Cisco released security updates to patch a denial-of-service zero-day in Adaptive Security Appliance (ASA) and Threat Defense (FTD) software that attackers are exploiting to remotely crash vulnerable firewall devices. Tracked as CVE-2026-76418, this high-severity vulnerability affects devices running ASA and FTD software with configurations containing the ‘webvpn’ keyword and SSL VPN enabled on at least […]
Apple backports CoreGraphics zero-day patches to older iPhones
Apple has backported security patches released last month to older iPhones and iPads, addressing a zero-day bug exploited in “extremely sophisticated” targeted attacks on iOS devices. Apple patched the same vulnerability in September for devices running iOS 26.7.1 and iPadOS 26.7.1, macOS Tahoe 26.7.1, and macOS Sequoia 15.8.1. Meta Product Security discovered this out-of-bounds write […]
Arista patches new VeloCloud Orchestrator zero-day exploited in attacks
Arista Networks released security updates to patch an actively exploited zero-day vulnerability affecting VeloCloud Orchestrator (VCO) On-Prem deployments. VCO is a web-based management portal that helps administrators configure, monitor, and manage VeloCloud SD-WANs (Software-Defined Wide Area Networks) and associated edge devices. Tracked as CVE-2026-114625, this critical-severity flaw can allow attackers with basic privileges, access to […]

BAE Systems cyberattack disrupts US federal court operations
The Administrative Office of the US Courts says a cyberattack on government contractor BAE Systems has taken down the notice system used by federal bankruptcy courts. In a Thursday press release, the Administrative Office of the US Courts said the BAE Systems cyberattack also halted the production and distribution of bankruptcy notices. “The Administrative Office […]
Palo Alto Networks warns of PAN-OS RCE flaw exploited in attacks
Palo Alto Networks has released security updates for a high-severity PAN-OS RCE zero-day, tracked as CVE-2026-0322, that has been exploited in attacks targeting firewalls. The vulnerability affects the PAN-OS management interface and lets authenticated attackers with network access execute code as root on vulnerable devices. Palo Alto Networks confirmed in a security advisory published Wednesday […]
Cisco patches new Secure Email Gateway zero-day exploited in attacks
Cisco has patched another actively exploited zero-day flaw in its Secure Email Gateway (SEG) that lets remote unauthenticated attackers execute commands with root privileges. Tracked as CVE-2026-76519, this vulnerability stems from a relative path traversal weakness in SEG’s Advanced Malware Protection (AMP) feature, caused by improper handling of email attachments. Threat actors can exploit this issue […]
CISA warns admins to immediately fix Ivanti flaw exploited as zero-day
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) urged security teams to immediately patch an Ivanti Connect Secure (ICS) flaw exploited in zero-day attacks since at least October 1st. Tracked as CVE-2026-104935, this high-severity authentication bypass vulnerability lets remote threat actors without privileges execute arbitrary commands on targeted ICS systems in low-complexity attacks that don’t […]
Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days
Today is Microsoft’s October 2026 Patch Tuesday, with security updates addressing a record-breaking 1,411 flaws, including one actively exploited and two publicly disclosed zero-day vulnerabilities. This Patch Tuesday addresses 70 “Critical” vulnerabilities, 57 of which are remote code execution, 11 are elevation of privileges, and 2 are spoofing. The approximate number of bugs in each […]