ransomware

BlackSuit ransomware extortion sites seized in Operation Checkmate
Law enforcement has seized the dark web extortion sites of the BlackSuit ransomware operation, which has targeted and breached the networks of hundreds of organizations worldwide over the past several years. The U.S. Department of Justice confirmed the takedown in an email earlier today, saying the authorities involved in the action executed a court-authorized seizure […]

Microsoft: SharePoint servers also targeted in ransomware attacks
A China-based hacking group is deploying Warlock ransomware on Microsoft SharePoint servers vulnerable to widespread attacks targeting the recently patched ToolShell zero-day exploit chain. Non-profit security organization Shadowserver is currently tracking over 420 SharePoint servers that are exposed online and remain vulnerable to these ongoing attacks. “Although Microsoft has observed this threat actor deploying Warlock and Lockbit ransomware in the past, Microsoft […]

Ukraine arrests suspected admin of XSS Russian hacking forum
The suspected administrator of the Russian-speaking hacking forum XSS.is was arrested by the Ukrainian authorities yesterday at the request of the Paris public prosecutor’s office. XSS.is is a Russian-speaking cybercrime forum that has been active since 2013 and is widely regarded as one of the major online hubs for cybercriminal activity, with over 50,000 registered users. The platform […]

CISA and FBI warn of escalating Interlock ransomware attacks
CISA and the FBI warned on Tuesday of increased Interlock ransomware activity targeting businesses and critical infrastructure organizations in double extortion attacks. Today’s advisory was jointly authored with the Department of Health and Human Services (HHS) and the Multi-State Information Sharing and Analysis Center (MS-ISAC) and it provides network defenders with indicators of compromise (IOCs) collected […]

UK to ban public sector orgs from paying ransomware gangs
The United Kingdom’s government is planning to ban public sector and critical infrastructure organizations from paying ransoms after ransomware attacks. The list of entities that would have to follow the new proposed legislation includes local councils, schools, and the publicly funded National Health Service (NHS). “Ransomware is estimated to cost the UK economy millions of […]
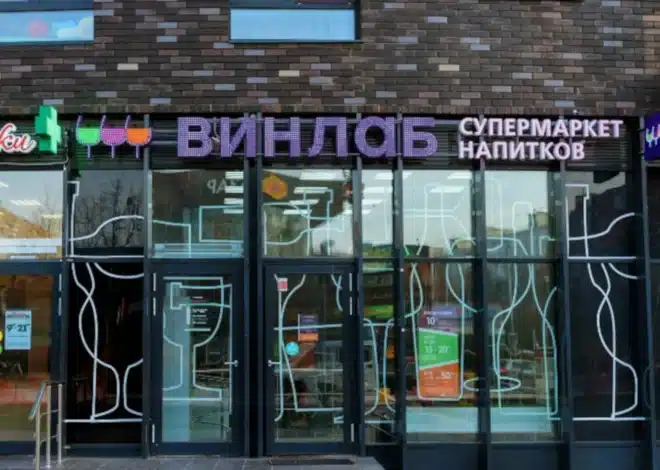
Russian alcohol retailer WineLab closes stores after ransomware attack
WineLab, the retail store of the largest alcohol company in Russia, has closed its stores following a cyberattack that is impacting its operations and causing purchase problems to its customers. Its parent company, Novabev Group, informed earlier this week that hackers had breached its IT systems. “On July 14, the group was subjected to an […]

New Phobos and 8base ransomware decryptor recover files for free
The Japanese police have released a Phobos and 8-Base ransomware decryptor that lets victims recover their files for free, with GeekFeed confirming that it successfully decrypts files. Phobos is a ransomware-as-a-service operation that launched in December 2018, enabling other threat actors to join as affiliates and utilize their encryption tool in attacks. In exchange, any […]

Police disrupt “Diskstation” ransomware gang attacking NAS devices
An international law enforcement action dismantled a Romanian ransomware gang known as ‘Diskstation,’ which encrypted the systems of several companies in the Lombardy region, paralyzing their businesses. The law enforcement operation codenamed ‘Operation Elicius’ was coordinated by Europol and also involved police forces in France and Romania. Diskstation is a ransomware operation that targets Synology […]

Interlock ransomware adopts FileFix method to deliver malware
Hackers have adopted the new technique called ‘FileFix’ in Interlock ransomware attacks to drop a remote access trojan (RAT) on targeted systems. Interlock ransomware operations have increased over the past months as the threat actor started using the KongTuke web injector (aka ‘LandUpdate808’) to deliver payloads through compromised websites. This shift in modus operandi was observed by researchers […]

Russian professional basketball player arrested for alleged role in ransomware attacks
Russian professional basketball player Daniil Kasatkin was arrested in France at the request of the United States for allegedly acting as a negotiator for a ransomware gang. Daniil Kasatkin is a Russian basketball player who briefly played NCAA basketball at Penn State before returning to Russia in 2019. In four seasons with MBA-MAI, he appeared in 172 […]