Legal
Canada orders TikTok to shut down over national risk concerns
The Canadian government has ordered the dissolution of TikTok Technology Canada following a multi-step review that provided information and evidence of the social media company posing a national risk. The decision also considered advice of Canada’s security and intelligence community as well as other government partners. It does not ban Canadian users’ access to the TikTok […]
Germany drafts law to protect researchers who find security flaws
The Federal Ministry of Justice in Germany has drafted a law to provide legal protection to security researchers who discover and responsibly report security vulnerabilities to vendors. When security research is conducted within the specified boundaries, those responsible will be excluded from criminal liability and the risk of prosecution. “Those who want to close IT […]
Interpol disrupts cybercrime activity on 22,000 IP addresses, arrests 41
Interpol announced it arrested 41 individuals and taken down 1,037 servers and infrastructure running on 22,000 IP addresses facilitating cybercrime in an international law enforcement action titled Operation Synergia II. The operation took place between April and August 2024, spanning 95 countries and resulting in 41 arrests of those linked to various crimes, including ransomware, […]
DDoS site Dstat.cc seized and two suspects arrested in Germany
The Dstat.cc DDoS review platform has been seized by law enforcement, and two suspects have been arrested after the service helped fuel distributed denial-of-service attacks for years. The seizure and arrests were conducted as part of “Operation PowerOFF,” an ongoing international law enforcement operation that targets DDoS-for-hire platforms, aka “booters” or “stressers,” to seize infrastructure and […]
CISA proposes new security requirements to protect govt, personal data
The U.S. Cybersecurity & Infrastructure Security Agency (CISA) is proposing security requirements to prevent adversary states from accessing American’s personal data as well as government-related information. The requirements are aimed at entities that engage in restricted transactions that involve bulk U.S. sensitive personal data or U.S. government-related data, especially if the info is exposed to “countries […]
Ukraine arrests rogue VPN operator providing access to Runet
Ukraine cyber police have arrested a 28-year-old man who operated a massive virtual private network (VPN) service, allowing people from within the country to access the Russian internet (Runet). Runet is the portion of the internet that includes Russian sites on the “.ru” and “.su” top-level domains, including government sites, social media platforms, search engines, and […]
Dutch police arrest admin of ‘Bohemia/Cannabia’ dark web market
An international law enforcement operation led to the arrest of one of the three administrators of the dual dark web market ‘Bohemia/Cannabia,’ known for hosting ads for drug sales and distributed denial of service (DDoS) attacks. The man was arrested at the Schiphol airport in Amsterdam on June 27, 2024, and electronic devices containing incriminating […]
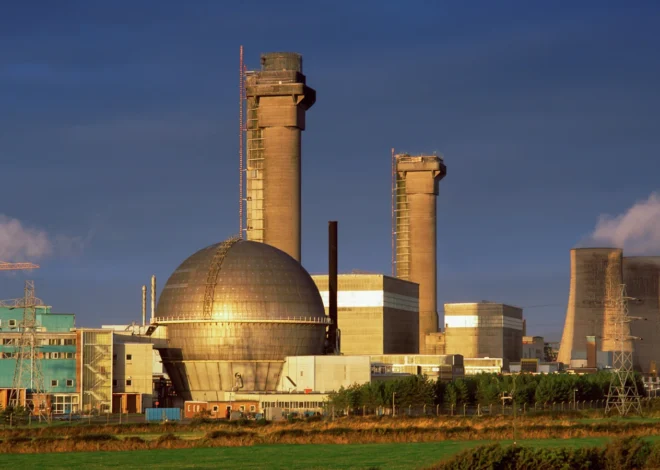
UK nuclear site Sellafield fined $440,000 for cybersecurity shortfalls
Nuclear waste processing facility Sellafield has been fined £332,500 ($440k) by the Office for Nuclear Regulation (ONR) for failing to adhere to cybersecurity standards and putting sensitive nuclear information at risk over four years, from 2019 to 2023. According to the ONR announcement, Sellafield failed to follow its own approved cybersecurity protocols by leaving multiple […]
Hacker charged for breaching 5 companies for insider trading
The U.S. Securities and Exchange Commission (SEC) charged Robert B. Westbrook, a U.K. citizen, with hacking into the computer systems of five U.S. public companies to access confidential earnings information and conduct insider trading. Westbrook then used this nonpublic information to make trades ahead of 14 earnings announcements between January 2019 and August 2020, earning […]
Ireland fines Meta €91 million for storing passwords in plaintext
The Data Protection Commission (DPC) in Ireland has fined Meta Platforms Ireland Limited (MPIL) €91 million ($100 million) for storing in plaintext passwords of hundreds of millions of users. The incident occurred in 2019. At the time, Meta disclosed it publicly and notified DPC, which initiated an investigation into the tech giant’s practices for storing […]