security
Vercel rolls out new protection against stolen session cookie attacks
Vercel is gradually rolling out Device Bound Session Credentials (DBSC) on its platform as a key defense against information stealer malware. The new feature, announced by Vercel’s CTO Malte Ubl on X, binds a login session to the user’s device with a private key stored in a TPM, so even if the session cookie is […]
Abandoned Popcorn Time app exposed millions of devices to RCE attacks
Researchers remotely disabled a vulnerable updater in the abandoned Time4Popcorn app, a fork of the Popcorn Time BitTorrent client, closing a security flaw that could have allowed attackers to execute malicious code with elevated privileges on millions of computers. The vulnerability, tracked as CVE-2026-30612, affects Windows and macOS updaters that contacted the app’s abandoned domain […]
Exposed GitLab project email addresses let attackers push code
Private GitLab email addresses that allow developers to push issues or tasks to a project are being deliberately exposed in READMEs, contributing guides, and support pages used to collect bug reports. The addresses are part of a built-in GitLab feature called “Email work item to this project” and contain a long-lived token tied to the […]

Hackers compromise 14,500 Dahua web cameras in 35-day campaign
In a large-scale campaign that researchers dubbed CameraSwarm, hackers compromised more than 14,500 Dahua IP cameras mostly in Ukraine and Russia. The operation ran for at least 35 days between June 17 and July 22, compromising devices by exploiting vulnerabilities, brute-forcing logins, and using offline recovery codes from serial numbers for cloud-registered cameras. Researchers at threat […]

Signal adds new security feature to thwart man-in-the-middle attacks
Signal has introduced Automatic Key Verification, a new security feature that gives users a new way to ensure their encrypted chats haven’t been intercepted. The new feature is part of a “key transparency” system that uses Cloudflare and Trail of Bits as trusted third-party independent auditors to verify the integrity of Signal conversations. “It works through a […]
Google Blogger locks hundreds of blogs in malware false positive
Google has locked hundreds of Blogger websites after a false positive claimed they violated its “Malware and Similar Malicious Content” policy, with some sites actually deleted from the platform. The issue began on August 4, and it appears to affect many legitimate blogs that do not host malware or have malicious scripts. As seen by […]
GitHub, PyPI add time-based defenses against supply chain attacks
GitHub and PyPI (Python Package Index) have introduced a time-based mechanism in the Dependabot dependency management tool to protect against supply-chain attacks and to limit their impact. Specifically, Dependabot comes with a default three-day cooldown setting, while PyPI will reject new files uploaded to releases older than 14 days. The measure comes after the two […]
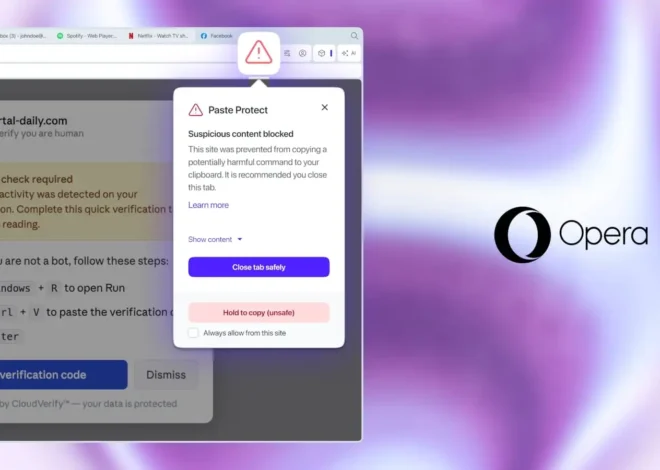
Opera rolls out Paste Protect feature to fight ClickFix attacks
Opera has introduced Paste Protect, a security feature designed to block ClickFix-style attacks that trick users into executing malicious commands through social engineering. ClickFix is a widely used technique where victims are deceived into copying dangerous code or commands to the clipboard and then executing them in the command-line interface. Typically, the ruse is a verification process or some […]
GitHub announces npm security changes to tackle supply-chain attacks
GitHub has announced that npm v12, expected next month, will introduce several security-focused changes aimed at blocking supply-chain attacks abusing behaviors triggered by the ‘npm install’ command. ‘npm install’ is the command used to download and install a project’s dependencies and run any install-related scripts defined by the packages. Developers execute it after cloning a […]
Signal adds security warnings for social engineering, phishing attacks
Signal has introduced new in-app confirmations and warning messages as additional safeguards against phishing and social engineering attempts that could lead to various forms of fraud. The purpose is to introduce enough friction that users get the time to evaluate the safety of an external request. Recently, there have been attacks targeting high-profile users with […]