Extensions
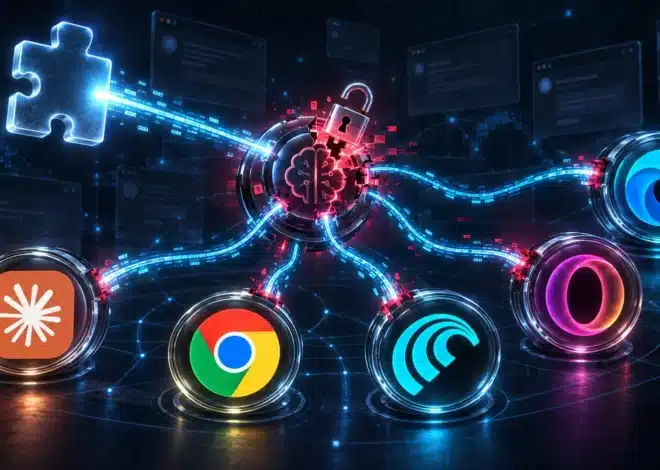
BragJack attacks hijack AI browser agents through malicious extensions
Security researcher Gal Weizman of Forever Security has disclosed a new attack technique that can hijack the AI assistants built into popular browsers using a single malicious browser extension. Dubbed BragJack, the proof-of-concept was demonstrated against five Chromium-based browsers or browser assistants: Google Chrome’s Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and Anthropic’s Claude […]
Microsoft Teams will let admins block custom file extensions
Microsoft Teams will soon let administrators tweak the list of file extensions commonly associated with malware and security threats to meet their company’s security requirements. This will come as an update to Weaponizable File Protection, a built-in Teams messaging safety feature that scans conversations and blocks chat or channel messages with dangerous, high-risk file attachments. As detailed in […]
Twitch extension with 30K installs exposes users’ OAuth tokens
A browser extension called Twitch Enhanced Viewer | JeetBot, available in the official Chrome and Firefox stores, sends users’ Twitch OAuth session tokens to a commercial bot service. The extension has more than 30,000 installs and is advertised as a legitimate third-party tool for Twitch that can block ads, force 1080p (full HD) playback, bypass […]
Chrome Web Store extensions caught stealing crypto, browser data
Multiple extensions for Google Chrome and Microsoft Edge delivered a malware framework that deployed modules to steal cryptocurrency, sensitive data, and browser history, and to inject ClickFix lures. Researchers say all 19 malicious modules uncovered in the campaign serve distinct purposes and are designed to be “highly extensible.” The operation was uncovered by application security […]
Hundreds of fake Chrome VPN extensions route traffic through a proxy
More than 737 browser extensions published on the Chrome Web Store impersonated well-known VPN and proxy services while routing users’ traffic through SOCKS5 proxies operated by a single provider. Some of the extensions impersonated dozens of established brands, including Proton VPN, NordVPN, Surfshark, ExpressVPN, and Cloudflare’s 1.1.1.1 public domain name system (DNS) resolver. Researchers at […]

77 Open VSX extensions found harvesting developer info
77 extensions on the Open VSX marketplace impersonated legitimate developer tools while transmitting information about the systems and development environments where they were installed. The so-called “evil twin” campaign was discovered by Manifold Security, which detected the extensions between July 26 and August 1, 2026. Researchers linked all 77 extensions to the same activity through a […]
Google Chrome may soon block New Tab hijacker extensions by default
Google is preparing a new Chrome security feature that would block policy-installed extensions from hijacking the New Tab page or changing the default search engine. GeekFeed spotted the protection in a chain of work-in-progress Chromium Gerrit changes. It has not shipped yet, but Google plans to enable it by default once the changes are approved. […]
CISA warns of actively exploited RCE flaws in Joomla extensions
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is warning that attackers are exploiting vulnerabilities in the iCagenda and Balbooa Forms extensions for Joomla to achieve remote code execution through arbitrary file uploads. The agency has categorized the flaws as a maximum priority, ordering federal agencies to apply available security updates and/or mitigations within three days, […]
Malicious Edge extension abuses Native Messaging as bridge to malware
A malicious Microsoft Edge extension dubbed ‘Edgecution’ has been used in a ransomware attack to escape the browser sandbox and deploy a Python-based backdoor. Access to the local system is obtained by leveraging the Chrome Native Messaging protocol that allows browser extensions to interact with native desktop applications, such as a password manager communicating with […]
GitHub confirms breach of 3,800 repos via malicious VSCode extension
GitHub has confirmed that roughly 3,800 internal repositories were breached after one of its employees installed a malicious VS Code extension. The company has since removed the unnamed trojanized extension from the VS Code marketplace and has secured the compromised device. “Yesterday we detected and contained a compromise of an employee device involving a poisoned […]