Police dismantle Kratos phishing platform, arrest developer
Authorities in Germany and the U.S. dismantled the central infrastructure of Kratos, a phishing-as-a-service (PhaaS) platform with global reach, and its developer was arrested in Indonesia. During the operation, authorities seized more than 200 servers, effectively disrupting the malicious service and rendering it inoperable. The action was led by Frankfurt’s Prosecutor General Office (ZIT), Germany’s […]
FakeGit campaign uses 7,600 GitHub repos to push SmartLoader malware
A large-scale operation dubbed ‘FakeGit’ is pushing SmartLoader and StealC malware through 7,600 malicious GitHub repositories that accumulated more than 14 million downloads. Over 800 repositories pretended to be AI skills or MCP servers and appeared more than 600 times in public AI registries and catalogs. This increased the likelihood of being discovered by AI […]
Critical SharePoint RCE flaw exploited to steal machine keys
Hackers are actively exploiting the critical CVE-2026-50522 vulnerability in Microsoft SharePoint to steal machine keys and maintain access even after affected servers are patched. An attacker obtaining them can create valid authentication tokens to impersonate users and access available resources such as SharePoint sites and documents with the privileges of the forged identity. Microsoft describes the […]
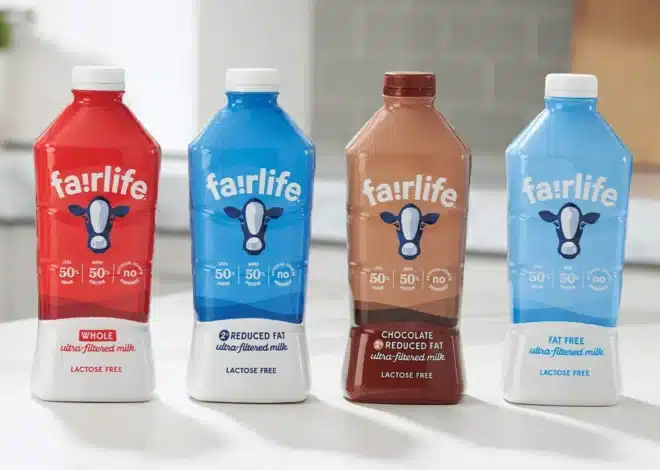
Anubis ransomware claims Coca-Cola Fairlife attack, threatens data leak
The Anubis ransomware gang has claimed responsibility for the cyberattack on Coca-Cola’s Fairlife dairy subsidiary, threatening to publish allegedly stolen corporate data unless the company pays a ransom. Fairlife is one of Coca-Cola’s dairy brands and produces a range of ultra-filtered milk products, protein shakes, and nutrition drinks sold throughout the United States. The company’s […]
Critical wp2shell WordPress flaws exploited to install webshells
Hackers are exploiting the “wp2shell” critical vulnerability suite (CVE-2026-63030 and CVE-2026-60137) affecting WordPress Core to deploy persistent webshells and install malicious plugins on affected servers. The critical exploit chain abuses the WordPress REST API’s batch-processing feature, allowing remote attackers to execute code on vulnerable installations without the need to authenticate. Although the technical details were not released, […]
US seizes over 1,000 websites in FIFA World Cup piracy crackdown
The U.S. Justice Department has seized more than 1,000 websites and blocked 1,970 domains used to stream FIFA World Cup 2026 matches without authorization. Law enforcement authorities identified the seized domains using leads provided by U.S. authorities, FIFA (Fédération Internationale de Football Association), the Motion Picture Association’s Alliance for Creativity and Entertainment (ACE), and multiple […]
Critical Palo Alto VPN bug now exploited by Qilin ransomware gang
The Qilin ransomware gang is exploiting a critical PAN-OS GlobalProtect authentication bypass flaw to breach victims’ networks, according to cybersecurity company Arctic Wolf. Palo Alto Networks addressed the vulnerability (CVE-2026-0257) on May 13 and warned that attackers had begun abusing it to breach corporate networks after Rapid7 reported observing it being exploited against numerous customers starting on […]

Microsoft shares manual fix for WSUS sync delays and timeouts
Microsoft has shared manual mitigations to help IT administrators fix Windows Server Update Services (WSUS) servers affected by a known issue that causes Windows Update scans to fail or time out. This known WSUS sync issue affects both client (Windows 10, version 1607 and later) and server (Windows Server 2012 and later) platforms. On impacted WSUS servers, […]
Windows LegacyHive zero-day flaw gets free, unofficial patches
Free unofficial patches are available for a recently disclosed Windows zero-day flaw that allows attackers to escalate privileges on up-to-date Windows systems. The vulnerability (dubbed LegacyHive and without a CVE ID for easy tracking) was found by a security researcher using the “Nightmare Eclipse” handle in the Windows User Profile Service. Nightmare Eclipse disclosed it the day […]
Estée Lauder discloses data breach via Oracle E-Business flaw
Cosmetics giant Estée Lauder is notifying customers of a data breach after hackers exploited a flaw in Oracle E-Business Suite that the company used for human resources (HR) operations. The company says that last month it identified an intrusion that had occurred on August 9, 2025, which led to the threat actor obtaining ” personal information of certain […]