Tech News
General news about the tech industry, trends, and major events.
Microsoft Teams vishing attacks lead to Chaos ransomware attacks
Threat actors are impersonating IT support staff in Microsoft Teams calls to gain remote access to corporate devices and deploy Chaos ransomware in attacks targeting North American organizations. Sophos tracks the campaign as STAC4749 and says it targeted dozens of organizations between February and June 2026. At least three of these intrusions led to the […]

Analog Devices discloses data breach, says operations unaffected
American semiconductor company Analog Devices announced that an unauthorized party accessed some of its systems and exfiltrated certain files. The company detected the incident on June 23 and reacted by activating its incident response protocols to limit the breach. External cybersecurity experts have been contracted to assist with the containment and investigation activities. Currently, there […]

Russian hackers exploit Exchange OWA zero-day for long-term mailbox access
The Russian state-sponsored hacking group Laundry Bear, also known as Void Blizzard, is exploiting an Exchange Outlook Web Access vulnerability in email campaigns to deliver a sophisticated backdoor called OWAReaper. Email security company Proofpoint spotted the activity a week ago targeting various organizations, including government entities in the U.S. and Europe, and companies in the […]
Anthropic confirms Claude is down worldwide
Claude is down for some users, with Anthropic confirming elevated errors across multiple AI models. The disruption is causing requests to fail with a “529 Overloaded” message, including in Claude and tools that rely on its API. Anthropic began investigating the outage at 7:49 p.m. UTC on July 29. At 8:33 p.m. UTC, the company said […]
Cisco warns of FMC static credential flaw exploited in zero-day attacks
Cisco is warning that a high-severity Secure Firewall Management Center (FMC) static credential vulnerability, tracked as CVE-2026-20316, was actively exploited in zero-day attacks to gain unauthorized access to vulnerable devices. The vulnerability is caused by static credentials for a low-privilege account built into Cisco Secure FMC Software. Cisco says an unauthenticated, remote attacker can use […]
Health-ISAC warns of rising ShinyHunters data theft attacks on healthcare
Health-ISAC, a cybersecurity information-sharing organization for the health sector, is warning healthcare and medical technology organizations of an observed increase in successful attacks by ShinyHunters. ShinyHunters is an extortion gang that primarily conducts supply chain and identity attacks to breach cloud SaaS and storage platforms in data theft attacks, Over the past two years, the threat […]

OpenAI agent used exposed credentials at 4 services in Hugging Face breach
In a new update, OpenAI says its AI models also used publicly exposed credentials to compromise accounts on four third-party services during the recent attack on Hugging Face, expanding the scope of the four-day security incident to other organizations. One account was used as an outbound relay and staging server during the attack, while another […]
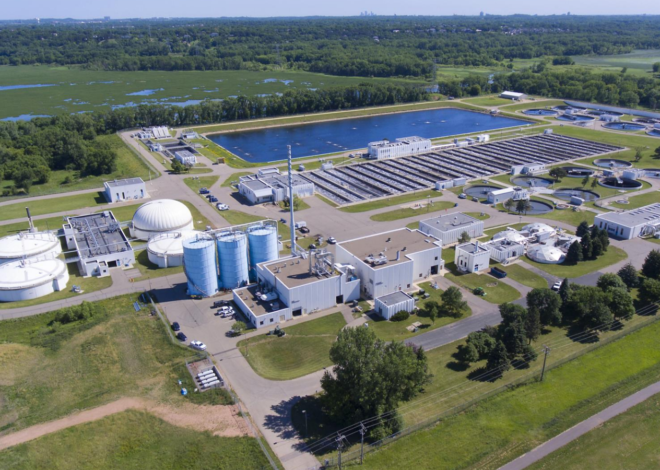
Hackers disrupt over 30 Minnesota water utilities in coordinated OT attack
The Minnesota IT Services (MNIT) agency activated its cybersecurity incident response capabilities across the entire state after hackers targeted more than 30 community water systems in “a coordinated cyberattack.” The attacks occurred on Sunday and Monday, July 26 and 27, and targeted operational technology (OT) systems at local water utilities. In a statement early Monday, […]
Windows 11 KB5101684 update released with 42 changes and fixes
Microsoft has released the KB5101684 preview cumulative update for Windows 11 24H2 and 25H2, which 42 bug fixes and additional feature improvements for the operating system. The KB5101684 update is part of the company’s optional non-security preview update schedule, which releases updates at the end of each month to test new fixes and features coming to the next month’s […]
CubePilot drone software dev hit by DNS hijacking to intercept traffic
CubePilot, an Australian firm that designs flight controllers for drones (UAVs), announced a severe operational disruption caused by a DNS hijacking attack. Hijacking domain name system (DNS) records allows threat actors to redirect users to their infrastructure, diverting traffic intended for a legitimate service. This exposes users to dangerous scenarios such as sensitive data interception, […]