Security
Stay informed with the latest developments in cybersecurity through our Security category. Discover in-depth news, analysis, and updates on emerging cyber threats, malware incidents, and major data breaches. Whether you’re a cybersecurity professional or just keen on protecting your digital footprint, find insights and trends that are shaping the future of online security here.
CISA orders feds to patch Zyxel flaw exploited for data theft
Attackers are now actively exploiting a high-severity vulnerability in Zyxel GS1900 series switches, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA). The flaw (tracked as CVE-2026-7273) stems from a stack-based buffer overflow in the CGI program that lets threat actors without privileges on the local area network (LAN) execute OS commands via maliciously […]
BigCommerce alerts merchants of data breach linked to Ribon apps
Ecommerce platform BigCommerce has alerted multiple merchants to data breaches after attackers compromised credentials for third-party Ribon applications and used them to inject malicious scripts into online stores. The cloud-based Software-as-a-Service (SaaS) ecommerce platform confirmed the credential compromise on September 17 and immediately removed the apps to protect its customers. UK-based online spirits vendor Master […]
CISA alerts of active exploitation of three Linux kernel flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is warning that hackers are exploiting three Linux kernel vulnerabilities, one of them rated critical. The three security issues were added separately last week and have severity ratings ranging from medium to critical. One of them, tracked as CVE-2025-39964, existed in the Linux kernel for 14 years. […]
WordPress Click2Shell flaw lets hackers execute PHP on the server
Technical details and a proof-of-concept exploit have been published for a new WordPress cross-site request forgery (CSRF) vulnerability dubbed ‘Click2Shell’ that affects the platform’s Core component. The security problem does not have an official identifier but was addressed last week with the release of WordPress version 7.1.1. It is a pre-authenticated remote code execution chain […]
Google fined €403 million over location data privacy violations
Ireland’s Data Protection Commission (DPC) has fined Google €403 million ($463M) for multiple GDPR violations related to processing users’ location data. The agency launched an investigation in February 2020 after receiving multiple complaints from consumer rights organizations. It examined three Google features that were active during the GDPR application period from May 25, 2018, through […]
Microsoft fixes broken Excel copy and paste for all Office users
Microsoft has fixed a known issue that causes copy-and-paste failures for Excel users after installing the September 2026 security updates. The bug was confirmed following a wave of customer reports on Reddit and the Microsoft Q&A forums that this month’s updates (including the KB5002914 security update) break copy-and-paste, autofill, and formula dragging in Excel. “In […]
Microsoft reminds admins to migrate Entra ID users to passkeys
Microsoft has reminded administrators to migrate Entra ID users to phishing-resistant methods, such as passkeys, to avoid sign-in disruptions after it retires SMS first-factor sign-in starting in February 2027. Admins also have alternatives, including QR code authentication, FIDO2 security keys, and other Entra ID-supported authentication methods. Before this date, organizations should ensure all users use […]
Malicious npm packages evade install-script defenses at runtime
An ongoing npm malware campaign involving the ‘indexed-btree’ package shows how threat actors bypass supply chain defenses by hiding malicious code in a package’s normal runtime behavior rather than in installation scripts. The package, spotted by Checkmarx researchers, attempts to impersonate the legitimate ‘sorted-btree’ library and has already amassed 2 million weekly downloads. The campaign may […]
Researchers escape OpenAI Codex sandbox to run commands on host
Security researchers found two ways out of the OpenAI Codex sandbox, one of them capable of running commands on a developer’s machine from Codex’s most locked-down mode, with no approval prompt and nothing shown on screen. Both flaws were reported to OpenAI on August 12 and fixed within eight days, according to Oren Yomtov of […]
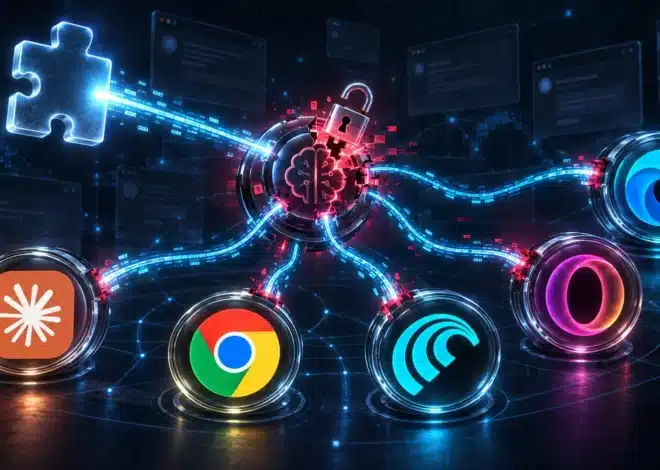
BragJack attacks hijack AI browser agents through malicious extensions
Security researcher Gal Weizman of Forever Security has disclosed a new attack technique that can hijack the AI assistants built into popular browsers using a single malicious browser extension. Dubbed BragJack, the proof-of-concept was demonstrated against five Chromium-based browsers or browser assistants: Google Chrome’s Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and Anthropic’s Claude […]