vulnerability
Hackers exploit critical Aviatrix Controller RCE flaw in attacks
Threat actors are exploiting a critical remote command execution vulnerability, tracked as CVE-2024-50603, in Aviatrix Controller instances to install backdoors and crypto miners. The Aviatrix Controller, part of the Aviatrix Cloud Networking Platform, enhances networking, security, and operational visibility for multi-cloud environments. It is used by enterprises, DevOps teams, network engineers, cloud architects, and managed […]
UK domain registry Nominet confirms breach via Ivanti zero-day
Nominet, the official .UK domain registry and one of the largest country code registries, has confirmed that its network was breached two weeks ago using an Ivanti VPN zero-day vulnerability. The company manages and operates over 11 million .uk, .co.uk, and .gov .uk domain names and other top-level domains, including .cymru and .wales. It also […]
Unpatched critical flaws impact Fancy Product Designer WordPress plugin
Premium WordPress plugin Fancy Product Designer from Radykal is vulnerable to two critical severity flaws that remain unfixed in the current latest version. With more than 20,000 sales, the plugin allows customization of product designs (e.g. clothing, mugs, phone cases) on WooCommerce sites by changing colors, transforming text, or modifying the size. While examining the […]
Ivanti warns of new Connect Secure flaw used in zero-day attacks
Ivanti is warning that hackers exploited a Connect Secure remote code execution vulnerability tracked as CVE-2025-0282 in zero-day attacks to install malware on appliances. The company says it became aware of the vulnerabilities after the Ivanti Integrity Checker Tool (ICT) detected malicious activity on customers’ appliances. Ivanti launched an investigation and confirmed that threat actors were actively […]
SonicWall urges admins to patch exploitable SSLVPN bug immediately
SonicWall is emailing customers urging them to upgrade their firewall’s SonicOS firmware to patch an authentication bypass vulnerability in SSL VPN and SSH management that is “susceptible to actual exploitation.” In an email sent to SonicWall customers and shared on Reddit, the firewall vendor says the patches are available as of yesterday, and all impacted customers should install them […]
New Mirai botnet targets industrial routers with zero-day exploits
A relatively new Mirai-based botnet has been growing in sophistication and is now leveraging zero-day exploits for security flaws in industrial routers and smart home devices. Exploitation of previously unknown vulnerabilities started in November 2024, according to Chainxin X Lab researchers who monitored the botnet’s development and attacks. One of the security issues is CVE-2024-12856, a […]
Vulnerable Moxa devices expose industrial networks to attacks
Industrial networking and communications provider Moxa is warning of a high-severity and a critical vulnerability that impact various models of its cellular routers, secure routers, and network security appliances. The two seurity issues allow remote attackers to get root privileges on vulnerable devices and to execute arbitrary commands, which could lead to arbitrary code execution. Risks […]
Nuclei flaw lets malicious templates bypass signature verification
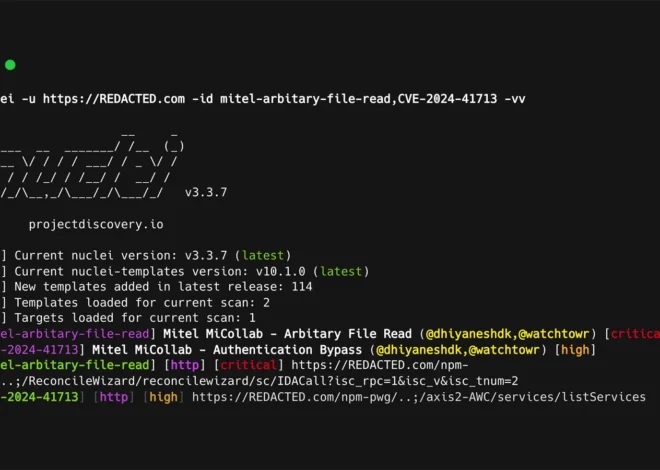
A now-fixed vulnerability in the open-source vulnerability scanner Nuclei could potentially allow attackers to bypass signature verification while sneaking malicious code into templates that execute on local systems. Nuclei is a popular open-source vulnerability scanner created by ProjectDiscovery that scans websites for vulnerabilities and other weaknesses. The project utilizes a template-based scanning system of over 10,000 […]
Hackers exploit Four-Faith router flaw to open reverse shells
Threat actors are exploiting a post-authentication remote command injection vulnerability in Four-Faith routers tracked as CVE-2024-12856 to open reverse shells back to the attackers. The malicious activity was discovered by VulnCheck, who informed Four-Faith about the active exploitation on December 20, 2024. However, it is unclear if security updates for the vulnerability are currently available. […]
Hackers exploit DoS flaw to disable Palo Alto Networks firewalls
Palo Alto Networks is warning that hackers are exploiting the CVE-2024-3393 denial of service vulnerability to disable firewall protections by forcing it to reboot. Leveraging the security issue repeatedly, however, causes the device to enter maintenance mode and manual intervention is required to restore it to normal operations. “A Denial of Service vulnerability in the DNS […]