Hackers targeting WhatsUp Gold with public exploit since August
Hackers have been leveraging publicly available exploit code for two critical vulnerabilities in the WhatsUp Gold network availability and performance monitoring solution from Progress Software. The two flaws exploited in attacks since August 30 are SQL injection vulnerabilities tracked as CVE-2024-6670 and CVE-2024-6671 that allow retrieving encrypted passwords without authentication. Despite the vendor addressing the security issues more than two […]
GitLab warns of critical pipeline execution vulnerability
GitLab has released critical updates to address multiple vulnerabilities, the most severe of them (CVE-2024-6678) allowing an attacker to trigger pipelines as arbitrary users under certain conditions. The release is for versions 17.3.2, 17.2.5, and 17.1.7 for both GitLab Community Edition (CE) and Enterprise Edition (EE), and patches a total of 18 security issues as part of the bi-monthly […]
Fortinet confirms data breach after hacker claims to steal 440GB of files
Cybersecurity giant Fortinet has confirmed it suffered a data breach after a threat actor claimed to steal 440GB of files from the company’s Microsoft Sharepoint server. Fortinet is one of the largest cybersecurity companies in the world, selling secure networking products like firewalls, routers, and VPN devices. The company also offers SIEM, network management, and EDR/XDR […]
Fake password manager coding test used to hack Python developers
Members of the North Korean hacker group Lazarus posing as recruiters are baiting Python developers with coding test project for password management products that include malware. The attacks are part of the ‘VMConnect campaign’ first detected in August 2023, where the threat actors targeted software developers with malicious Python packages uploaded onto the PyPI repository. According […]
Adobe fixes Acrobat Reader zero-day with public PoC exploit
A cybersecurity researcher is urging users to upgrade Adobe Acrobat Reader after a fix was released yesterday for a remote code execution zero-day with a public in-the-wild proof-of-concept exploit. The flaw is tracked as CVE-2024-41869 and is a critical use after free vulnerability that could lead to remote code execution when opening a specially crafted PDF […]
WordPress.org to require 2FA for plugin developers by October
Starting October 1st, WordPress.org accounts that can push updates and changes to plugins and themes will be required to activate two-factor authentication (2FA) on their accounts. The decision is part of the platform’s plugin review team effort to reduce the risk of unauthorized access, which could lead to supply-chain attacks. “Accounts with commit access can push […]
RansomHub ransomware abuses Kaspersky TDSSKiller to disable EDR software
The RansomHub ransomware gang has been using TDSSKiller, a legitimate tool from Kaspersky, to disable endpoint detection and response (EDR) services on target systems. After taking down the defenses, RansomHub deployed the LaZagne credential-harvesting tool to extract logins from various application databases that could help move laterally on the network. TDSSKiller abused in ransomware attacks Kaspersky […]
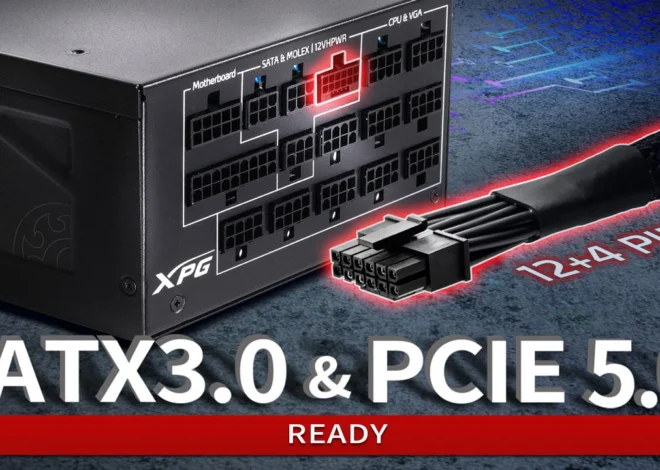
What Is ATX 3.0? Everything To Know About ATX3 Power Supplies
The often overlooked power supply unit (PSU) of our computers is getting a major upgrade with the introduction of ATX 3.0. The new ATX 3.0 power supply unit features a 16-pin power cable and comes with a range of new features, marking a significant advancement in PC power supplies. This upgrade is set to revolutionize […]
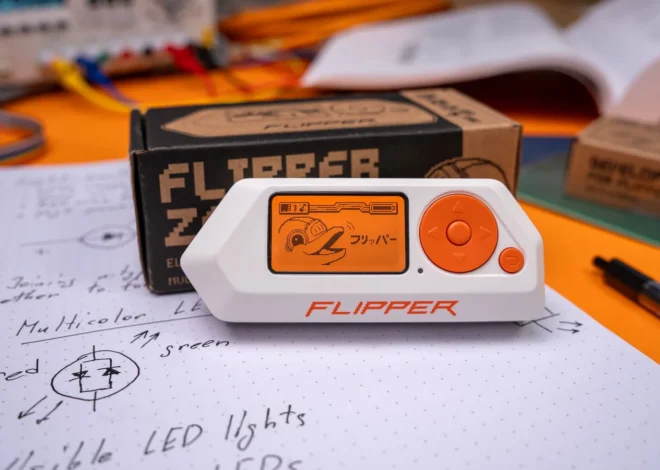
Flipper Zero releases Firmware 1.0 after three years of development
After three years of development, the Flipper Zero team has announced the release of the first major firmware version for the portable, customizable hacking device. Flipper Zero is a programmable device for pentesters that has faced controversy after users posted videos online showcasing illegal activities. Because of this, the gadged has been banned or restricted in some […]
New PIXHELL acoustic attack leaks secrets from LCD screen noise
A novel acoustic attack named ‘PIXHELL’ can leak secrets from air-gapped and audio-gapped systems, and without requiring speakers, through the LCD monitors they connect to. In a PIXHELL attack, malware modulates the pixel patterns on LCD screens to induce noise in the frequency range of 0-22 kHz, carrying encoded signals within those acoustic waves that can […]