Critical UniFi OS bug lets hackers gain root without authentication
Attackers can chain three already fixed vulnerabilities in the Ubiquiti UniFi OS server to execute remote code with root privileges and without authentication. The security issues are tracked as CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910. They have been addressed in May and impact UniFi OS Server versions 5.0.6 and earlier. While all three flaws received the maximum severity […]
Check Point links VPN zero-day attacks to Qilin ransomware gang
Israeli cybersecurity company Check Point has released security updates to patch a critical flaw affecting Remote Access VPN and Mobile Access deployments, which was exploited in zero-day attacks. Tracked as CVE-2026-50751, this vulnerability can be exploited by unauthenticated, remote attackers to bypass authentication on targeted Mobile Access / SSL VPNs, Remote Access VPNs, or Spark firewalls […]
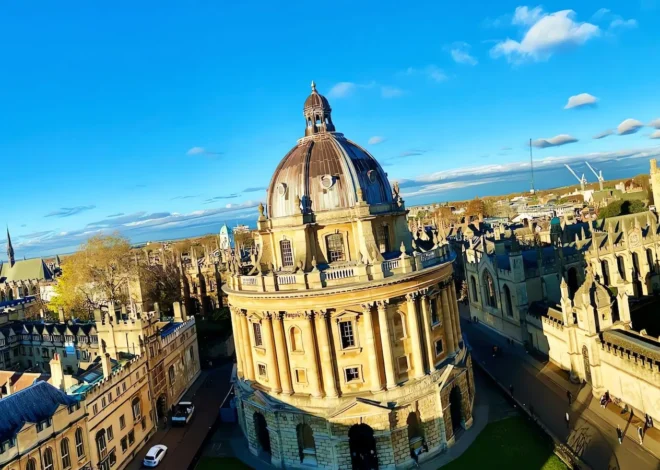
Oxford University discloses data breach after careers platform hack
The University of Oxford disclosed a new data breach last week after being informed by its third-party provider, Group GTI, that its CareerConnect career services platform had been compromised. This platform is also used by other UK educational organizations, such as King’s College London and the University of Manchester, to run their institution-specific career hubs. […]
Over 20,000 Instagram accounts stolen in Meta AI support hack
Meta has revealed that over 20,000 Instagram users had their accounts hijacked in a recent incident where attackers used Meta’s AI-powered support system to reset passwords. As GeekFeed reported one week ago, the threat actors exploited a flaw in the company’s High Touch Support (HTS) tool, an AI-assisted support system that helps users regain access after being locked out of […]
Hands on with Intelligent Terminal, an AI-powered Windows Terminal
Microsoft has created an open-source fork of Windows Terminal called “Intelligent Terminal,” and it allows you to use AI directly inside Terminal without interfering with the regular session. Microsoft describes the Intelligent Terminal as a built-in assistant that can help you explain errors, draft commands, and fix problems without leaving the terminal. First, the agent […]
C0XMO botnet spreads via DD-WRT router flaw, kills rival malware
A new variant of the Gafgyt botnet called C0XMO is targeting DD-WRT router firmware and can move to other device types with various CPU architectures. The researchers found samples for ARM, MIPS, PowerPC, SuperH, x86, x86_64, and other architectures, featuring exploits for DVRs, routers, video management platforms, and Android-based devices. The botnet was seen targeting […]
Silent Ransom Group targets law firms with fake IT support calls
The Silent Ransom Group extortion gang is actively targeting U.S. law firms and professional services organizations in social engineering attacks that often lead to data theft within hours of initial contact, according to a new report by cybersecurity firm Mandiant. The report follows an FBI FLASH advisory published last week warning that the Silent Ransom […]
Critical Everest Forms Pro flaw exploited to take over WordPress sites
Hackers are actively exploiting a critical vulnerability (CVE-2026-3300) in the Everest Forms Pro plugin, which lets them take complete control of a WordPress website. The security issue affects versions 1.9.12 and earlier of the plugin and can be leveraged without authentication to execute arbitrary code on the server. Everest Forms Pro is a commercial add-on […]
Suspicious Polyfill login prompts pop up on Toshiba, Muji websites
Tech giant Toshiba and mega-retailer Muji warned visitors that suspicious sign-in screens popping up on their websites could collect credentials. Both Japanese companies advised users who entered their account login data in the authentication screens to change their passwords to access the service. The login pop-ups were generated by the external service hosted at polyfill[.]io, […]
CISA: Hackers now exploit SolarWinds Serv-U flaw to crash servers
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned today that hackers are now actively exploiting a recently patched high-severity SolarWinds Serv-U flaw to crash servers. Serv-U is the company’s Windows and Linux file transfer software that offers Managed File Transfer (MFT) and FTP server capabilities, which allow users to securely exchange files via HTTP/HTTPS, […]