Pharma giant Novo Nordisk discloses breach of clinical trials data
Danish pharmaceutical giant Novo Nordisk, the world’s largest producer of insulin, disclosed a data breach affecting patient information from some clinical trials. Founded in 1923, Novo Nordisk now employs around 67,900 people across 80 offices worldwide and is the maker of viral GLP-1 receptor agonist drugs Wegovy and Ozempic. The company revealed on Thursday that attackers gained access […]
CISA orders feds to patch actively exploited Ivanti flaw by Sunday
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) ordered government agencies to patch an actively exploited Ivanti Sentry flaw within three days, as mandated by the newly issued Binding Operational Directive (BOD) 26-04. Tracked as CVE-2026-10520, this maximum-severity vulnerability was found in Ivanti’s security gateway appliance (formerly known as MobileIron Sentry) and stems from an OS […]
Over 73,000 French govt employees affected in Tchap messenger breach
The French government revealed that a recent breach of its Tchap encrypted messaging platform affects the accounts of over 73,000 employees in the French public sector. DINUM, the French government’s digital affairs directorate, disclosed on Monday that a threat actor gained access to the Tchap platform using a compromised user account and notified France’s data protection authority (CNIL) due to the […]
Japanese energy firm loses drive with data of 10.9 million clients
Kyushu Electric Power Co., Inc. has disclosed a physical security incident that affects private data of more than 10 million customers. In an official announcement, the company explains that the IT staff regularly performs backups to manage server storage. Due to capacity constraints, on April 27 an external storage device was used for the task. The drive […]
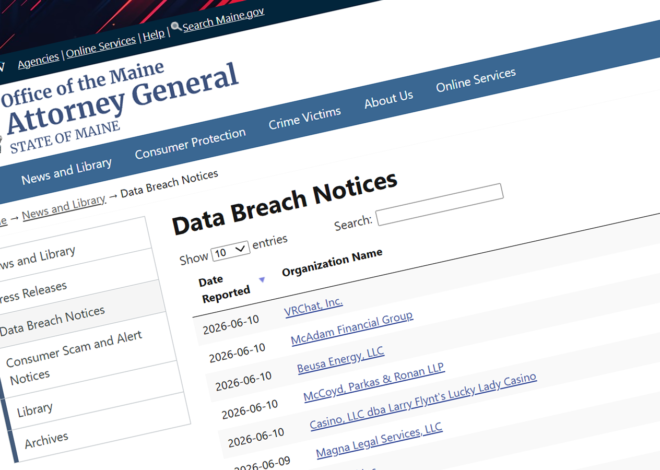
Maine breach portal abused to publish fake data breach disclosures
In an unusual misinformation campaign, fraudulent data breach disclosures were submitted to Maine’s official breach portal and publicly posted before their legitimacy could be verified, prompting companies to deny the claims. A notice allegedly filed by multiplayer social virtual reality platform VRChat is the most recent entry in the state Attorney General’s breach disclosure database. […]
Oracle mitigates PeopleSoft zero-day exploited in data theft attacks
Oracle is warning about a critical PeopleSoft Suite zero-day vulnerability tracked as CVE-2026-35273 that allows unauthenticated remote code execution, with the flaw actively exploited in ShinyHunter data theft attacks. The flaw is within Oracle PeopleSoft PeopleTools and has a CVSS base score of 9.8. “This Security Alert addresses vulnerability CVE-2026-35273 in Oracle PeopleSoft PeopleTools. Oracle PeopleSoft Enterprise Applications […]
Authorities dismantle ‘AudiA6’ ransomware crypto-laundering service
Law enforcement has dismantled the “AudiA6” cryptocurrency service allegedly used by ransomware actors and other cybercriminals to launder more than $380 million. Europol says that the service has been linked to more than 15 distinct international investigations of ransomware attacks. It is believed that the platform acted as a central money laundering hub between 2022 and 2025. […]
Coupang hit with record $409 million data breach fine in Korea
The Personal Information Protection Commission (PIPC), South Korea’s data protection regulator, has fined e-commerce giant Coupang a record 624.6 billion won (roughly $409 million) following a massive data breach affecting more than 37 million customers. Subsidiary Coupang Fulfillment Service was also fined 248 million won for unlawfully collecting, using, and handling customers’ personal and sensitive […]
CISA tells govt agencies to patch critical exploited flaws in 3 days
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) announced a new Binding Operational Directive, 26-04, that prioritizes security updates for Federal Civilian Executive Branch (FCEB) agencies. The directive aims to reduce the threat of cyberattacks targeting the public sector by requiring agencies to remediate high-risk vulnerabilities within accelerated timeframes, in some cases as little as […]
Microsoft fixes BitLocker recovery bug on Windows Server 2025
Microsoft has resolved a known issue causing some Windows Server 2025 devices to boot into BitLocker recovery after installing the April 2026 security update. The BitLocker security feature encrypts storage drives to prevent data theft and will typically force Windows computers to enter recovery mode after hardware changes or events, such as TPM (Trusted Platform […]