GitLab
CISA: Hackers now exploit max severity GitLab flaw in attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned that hackers are now exploiting a maximum-severity GitLab vulnerability in attacks. GitLab’s DevSecOps platform is used by over 50% of Fortune 100 companies and has over 30 million registered users worldwide. The security flaw (tracked as CVE-2026-85706) stems from missing authentication enforcement and improper path confinement […]
GitLab urges users to patch max severity path traversal flaw
GitLab urged users on Thursday to patch their servers immediately against a maximum-severity path traversal vulnerability tracked as CVE-2026-85706. The security flaw, discovered by a security researcher using the ‘s3ntago‘ handle and reported via GitLab’s HackerOne bug bounty program, stems from improper path confinement and missing authentication enforcement in the repository commits API. Unauthenticated attackers can […]

CISA warns of five-year-old GitLab flaw exploited in attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) ordered government agencies to patch their systems against a five-year-old GitLab vulnerability that is actively being exploited in attacks. GitLab patched this server-side request forgery (SSRF) flaw (tracked as CVE-2021-39935) in December 2021, saying it could allow unauthenticated attackers with no privileges to access the CI Lint API, which is […]
GitLab warns of high-severity 2FA bypass, denial-of-service flaws
GitLab has patched a high-severity two-factor authentication bypass impacting community and enterprise editions of its software development platform. Tracked as CVE-2026-0723, this vulnerability stems from an unchecked return value weakness in GitLab’s authentication services, allowing attackers who know the target’s account ID to circumvent two-factor authentication. “GitLab has remediated an issue that could have allowed an […]

Public GitLab repositories exposed more than 17,000 secrets
After scanning all 5.6 million public repositories on GitLab Cloud, a security engineer discovered more than 17,000 exposed secrets across over 2,800 unique domains. Luke Marshall used the TruffleHog open-source tool to check the code in the repositories for sensitive credentials like API keys, passwords, and tokens. The researcher previously scanned Bitbucket, where he found 6,212 secrets spread over 2.6 million repositories. […]

GitLab patches high severity account takeover, missing auth issues
GitLab has released security updates to address multiple vulnerabilities in the company’s DevSecOps platform, including ones enabling attackers to take over accounts and inject malicious jobs in future pipelines. The company released GitLab Community and Enterprise versions 18.0.2, 17.11.4, and 17.10.8 to address these security flaws and urged all admins to upgrade immediately. “These versions […]

Education giant Pearson hit by cyberattack exposing customer data
Education giant Pearson suffered a cyberattack, allowing threat actors to steal corporate data and customer information, GeekFeed has learned. Pearson is a UK-based education company and one of the world’s largest providers of academic publishing, digital learning tools, and standardized assessments. The company works with schools, universities, and individuals in over 70 countries through its […]

Europcar GitLab breach exposes data of up to 200,000 customers
A hacker breached the GitLab repositories of multinational car-rental company Europcar Mobility Group and stole source code for Android and iOS applications, as well as some personal information belonging to up to 200,000 customers. The actor tried to extort the company by threatening to publish 37GB of data that includes backups and details about the […]
GitLab patches critical authentication bypass vulnerabilities
GitLab released security updates for Community Edition (CE) and Enterprise Edition (EE), fixing nine vulnerabilities, among which two critical severity ruby-saml library authentication bypass flaws. All flaws were addressed in GitLab CE/EE versions 17.7.7, 17.8.5, and 17.9.2, while all versions before those are vulnerable. GitLab.com is already patched, and GitLab Dedicated customers will be updated […]
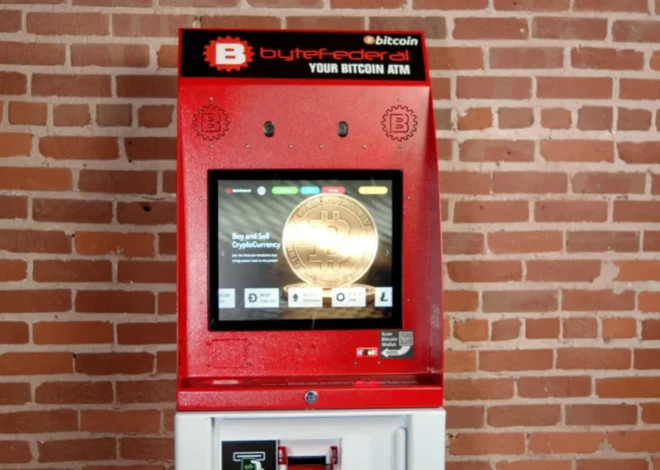
Bitcoin ATM firm Byte Federal hacked via GitLab flaw, 58K users exposed
US Bitcoin ATM operator Byte Federal has disclosed a data breach that exposed the data of 58,000 customers after its systems were breached using a GitLab vulnerability. Byte Federal is the largest US operator of Bitcoin ATMs across the United States, with over 1,200 ATMs located in forty-two states, allowing people to exchange cash for cryptocurrency. […]