ClickFix
Custom ChatGPTs push ClickFix attacks to deploy RAT malware
Custom variants of OpenAI’s ChatGPT promoted in sponsored Google results are directing unsuspecting users to malicious sites that use ClickFix attacks to deliver malware. The threat actor is abusing the legitimate feature in the AI platform that lets users create a version of ChatGPT tailored for a specific task that combines instructions, extra knowledge, and […]
Placeholder domain used in dev docs now serves ClickFix attacks
The “third-party.com” domain, commonly used as a placeholder in developer documentation and code examples, is serving a fake Cloudflare verification page that attempts to trick Windows users into executing PowerShell commands. The domain third-party.com has long been used in documentation to represent an arbitrary external website, API, or service, similar to how developers use domains such […]
Brevo supply-chain attack injected ClickFix scripts on customer sites
Brevo confirmed that attackers stole a Cloudflare API key and used it to inject malicious ClickFix scripts into its websites and JavaScript files embedded on customer sites to distribute malware. The customer relationship management and digital marketing company says the attackers used the API key to create a malicious Cloudflare Worker that modified content at […]
Hackers hijack HBO Max Reddit account to push malware in ClickFix ads
Hackers compromised HBO Max’s official Reddit account and used it to push malicious ads that launched ClickFix attacks to infect Windows and macOS devices with information-stealing malware. Security researchers at Hudson Rock and ADAMnetworks analyzed the campaign and say the verified u/hbomax Reddit account was hijacked and used to launch 108 malicious advertisements over about 48 […]
Over 5,400 hacked sites serve ClickFix payloads stored on the blockchain
A massive cybercriminal operation is leveraging thousands of compromised small-business websites to deliver ClickFix payloads stored in smart contracts on the BNB Smart Chain (BSC). Over the past months, researchers identified more than 5,400 hacked websites, most of them built on WordPress and PrestaShop. The initial compromise method remains unknown, but each site was injected […]
Microsoft warns of TerminalFix attacks deploying reverse tunnels
A new ClickFix variant dubbed TerminalFix uses fake Cloudflare CAPTCHA prompts on compromised websites to trick victims into executing malicious PowerShell commands in Windows Terminal. Unlike typical ClickFix attacks that often lead to infostealer malware infections, this campaign uses a multi-stage intrusion chain that ultimately gives attackers a reverse tunnel into the victim’s internal network. TerminalFix […]

New DOUBLECUP ClickFix service hides malware in browser cache images
A new Russian loader-as-a-service named DOUBLECUP uses ClickFix attacks to hide malicious code in PNG images cached by victims’ browsers, ultimately delivering CountLoader to Windows and macOS devices and a new remote access trojan named DeviceManager to Windows systems. SOCRadar’s Threat Research Unit says DOUBLECUP has operated since early June 2026, providing customers with licenses […]
Steam forum ClickFix attacks infect gamers with XMRig cryptominers
Steam discussion forums are being abused in ClickFix attacks that pretend to be fixes for game and computer problems but actually infect devices with cryptominers. GeekFeed learned of the campaign from a reader, who told us threat actors are creating random Steam accounts to post what appears to be helpful fixes for people’s posts about games […]
Microsoft warns of surge in ACR Stealer attacks on customers
Microsoft has observed a surge in attacks using the ACR Stealer malware to steal browser-stored passwords, authentication tokens, and sensitive documents from its enterprise customers. Between late April and mid-June, the threat actor used the ClickFix social-engineering method, WebDAV servers, and the MSHTA (Microsoft HTML Application Host) utility to deliver the info-stealing payload. ACR Stealer […]
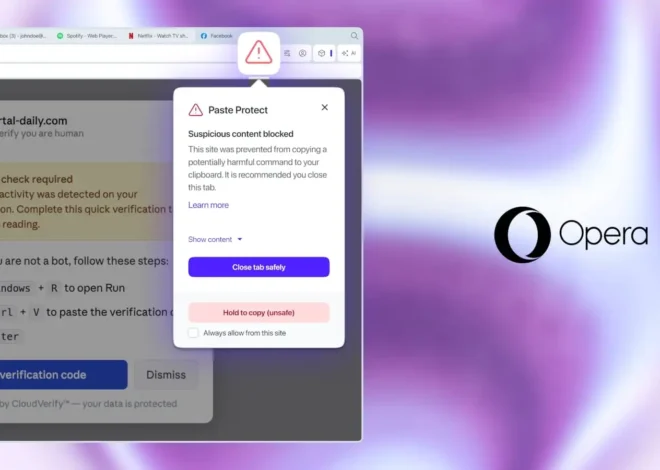
Opera rolls out Paste Protect feature to fight ClickFix attacks
Opera has introduced Paste Protect, a security feature designed to block ClickFix-style attacks that trick users into executing malicious commands through social engineering. ClickFix is a widely used technique where victims are deceived into copying dangerous code or commands to the clipboard and then executing them in the command-line interface. Typically, the ruse is a verification process or some […]