Chinese hackers target telcos with new Linux, Windows malware
A Chinese cyber-espionage campaign has been targeting telecommunications providers with newly discovered Linux and Windows malware dubbed Showboat and JFMBackdoor, respectively. The operation has been active since at least mid-2022 and targeted organizations across the Asia Pacific and parts of the Middle East. It was attributed to the Calypso threat group, also tracked as Red […]
Max severity Cisco Secure Workload flaw gives Site Admin privileges
Cisco has released security updates to address a maximum-severity Secure Workload vulnerability that allows attackers to gain Site Admin privileges. Formerly known as Cisco Tetration, Cisco Secure Workload helps admins reduce their network’s attack surface through zero trust microsegmentation and stop lateral movement to keep business applications safe. Tracked as CVE-2026-20223, the security flaw was found […]
Police seize “First VPN” service used in ransomware, data theft attacks
A virtual private network service called ‘First VPN,’ used in ransomware and data theft attacks, has been taken offline in a joint international law enforcement operation. Authorities have seized dozens of First VPN servers located in 27 countries, arrested the administrator, and conducted a house search in Ukraine. The VPN service was advertised on various […]
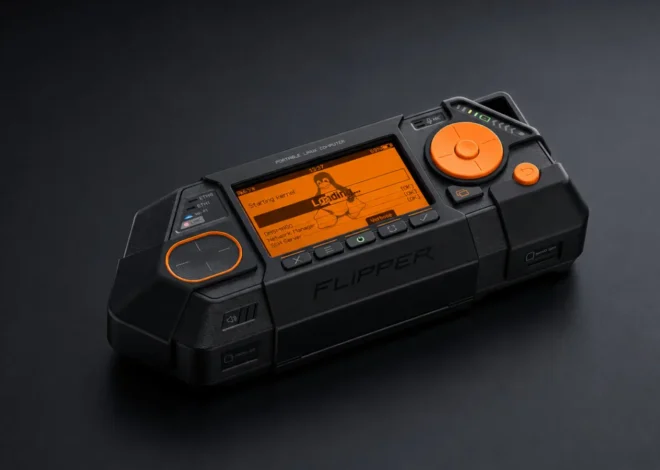
Flipper One project needs community help to build open Linux platform
Flipper Devices, the maker of the Flipper Zero pentesting tool, is asking the community to help build Flipper One, an open Linux platform for connected devices. Unlike Flipper Zero, which focuses on offline access control and radio technologies such as NFC, RFID, infrared, and sub-GHz communications, the Flipper One project is designed as a high-performance, Linux-based […]
Microsoft warns of new Defender zero-days exploited in attacks
On Wednesday, Microsoft started rolling out security patches for two Defender vulnerabilities that have been exploited in zero-day attacks. The first one, tracked as CVE-2026-41091, is a privilege escalation security flaw affecting Microsoft Malware Protection Engine 1.1.26030.3008 and earlier, which provides the scanning, detection, and cleaning capabilities for Microsoft antivirus and antispyware software. This flaw stems […]
GitHub links repo breach to TanStack npm supply-chain attack
GitHub says the hackers who breached 3,800 internal repositories gained access via a malicious version of the Nx Console VS Code extension, compromised in last week’s TanStack npm supply-chain attack. This attack is attributed to the TeamPCP threat group and began with the compromise of dozens of TanStack and Mistral AI npm packages, then quickly extended to other […]

Ukraine identifies infostealer operator tied to 28,000 stolen accounts
The Ukrainian cyberpolice, working in conjunction with U.S. law enforcement, has identified an 18-year-old man from Odesa suspected of running an infostealer malware operation targeting users of an online store in California. According to the Ukrainian police, the threat actor used information-stealing malware between 2024 and 2025 to infect users’ devices and steal browser sessions […]
Hackers bypass SonicWall VPN MFA due to incomplete patching
Threat actors brute-forced VPN credentials and bypassed multi-factor authentication (MFA) on SonicWall Gen6 SSL-VPN appliances to deploy tools used in ransomware attacks. During the intrusions, the hacker took between 30 and 60 minutes to log in, do network reconnaissance, test credential reuse on internal systems, and log out. SonicWall warned in a security advisory for […]
Grafana breach caused by missed token rotation after TanStack attack
The Grafana data breach was caused by a single GitHub workflow token that slipped through the rotation process following the TanStack npm supply-chain attack last week. In the ongoing Shai-Hulud malware campaign attributed to TeamPCP hackers, dozens of TanStack packages infected with credential-stealing code were published on the npm index, compromising developer environments, including Grafana’s. When the malicious […]
Max-severity flaw in ChromaDB for AI apps allows server hijacking
A max-severity vulnerability in the latest Python FastAPI version of the ChromaDB project allows unauthenticated attackers to run arbitrary code on exposed servers. The flaw is tracked as CVE-2026-45829 and was reported to ChromaDB on February 17. It received the maximum severity score from HiddenLayer, the company that discovered it. ChromaDB is an open-source vector database and AI retrieval […]