Claude Fable 5 isn’t permanently leaving subscriptions, Anthropic says
Anthropic says Claude Fable 5 won’t be accessible via Claude subscriptions after July 7, but it’s not a permanent change, and the company expects the model to return outside the usage-based plan soon. Fable 5 was recently restored after the US government lifted export controls on Anthropic’s most powerful models, Fable 5 and Mythos 5. As […]
Claude Fable relaunch disappoints users with nerfed performance
Claude Fable, the company’s most powerful model, is now available to all users, but early impressions are disappointing, as it appears to be nowhere near the original release. When the Department of Commerce announced that it was lifting the ban on Claude Fable, I was holding my breath and counting seconds for the model to show […]
Google loses final appeal to overturn €4.1 billion EU fine
Court of Justice of the European Union (CJEU) has dismissed Google’s final appeal against a €4.1 billion ($4.7 billion) antitrust fine over the company’s use of Android to promote its Chrome browser and search service. This is the conclusion of a European Commission decision in 2018 that Google abused its dominant market position by using Android agreements […]
Microsoft fixes bug that removed Copilot buttons in Outlook
Microsoft has fixed a known issue causing the Copilot Chat or Copilot buttons in Classic Outlook to disappear for Windows users with the Copilot Chat (Basic) license. As the company explains in a recent support document, affected users may no longer see Copilot buttons on the side navigation and above the ribbon. Those affected may also […]
Cisco finally confirms attackers exploiting Unified CM flaw
Cisco confirmed that attackers are now exploiting a Unified Communications Manager (Unified CM) vulnerability patched in early June. Unified CM (formerly known as Cisco CallManager) is the central control system for Cisco IP telephony systems, handling call routing, device management, and telephony features. Threat actors without privileges can exploit the vulnerability (CVE-2026-20230) remotely in low-complexity […]
CISA: Microsoft SharePoint RCE flaw now actively exploited
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned on Wednesday that attackers have begun exploiting a high-severity Microsoft SharePoint remote code execution vulnerability. Tracked as CVE-2026-45659, this security flaw stems from a deserialization of untrusted data weakness, and it allows attackers with low privileges to execute arbitrary code on unpatched SharePoint servers in low-complexity attacks […]
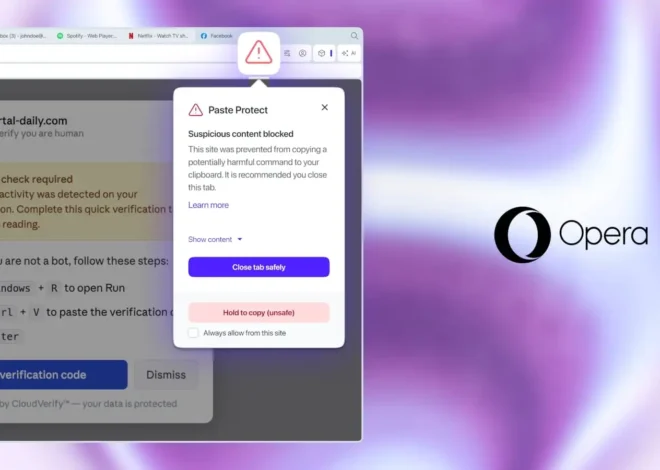
Opera rolls out Paste Protect feature to fight ClickFix attacks
Opera has introduced Paste Protect, a security feature designed to block ClickFix-style attacks that trick users into executing malicious commands through social engineering. ClickFix is a widely used technique where victims are deceived into copying dangerous code or commands to the clipboard and then executing them in the command-line interface. Typically, the ruse is a verification process or some […]
Alleged Scattered Spider hacker extradited to the United States
A dual United States and Estonian citizen has been extradited to the U.S. to face charges alleging he was a member of the Scattered Spider hacking collective. 19-year-old Peter Stokes (who used the online handles “Bouquet,” “Spencer,” and “Jordan”) was arrested in Finland on April 10 while attempting to board a flight to Japan at Helsinki’s […]
Medtronic notifies customers impacted by ShinyHunters data breach
Healthcare device firm Medtronic is notifying affected customers about a data breach that exposed their personal data to an unauthorized third party. The company previously confirmed that its IT systems were compromised by hackers, and the infamous data extortion group ‘ShinyHunters’ claimed the attack. The threat actor said that they were holding 9 million Medtronic records with […]
FortiBleed credential-theft campaign linked to Lynx ransomware
The massive FortiBleed credential theft campaign has been linked to the INC and Lynx ransomware operations, suggesting the stolen Fortinet credentials were intended to fuel future network intrusions. Earlier this month, a server containing credentials stolen from more than 73,000 Fortinet devices was discovered exposed on the internet. Researchers found the server contained downloaded FortiGate […]