Security
Stay informed with the latest developments in cybersecurity through our Security category. Discover in-depth news, analysis, and updates on emerging cyber threats, malware incidents, and major data breaches. Whether you’re a cybersecurity professional or just keen on protecting your digital footprint, find insights and trends that are shaping the future of online security here.
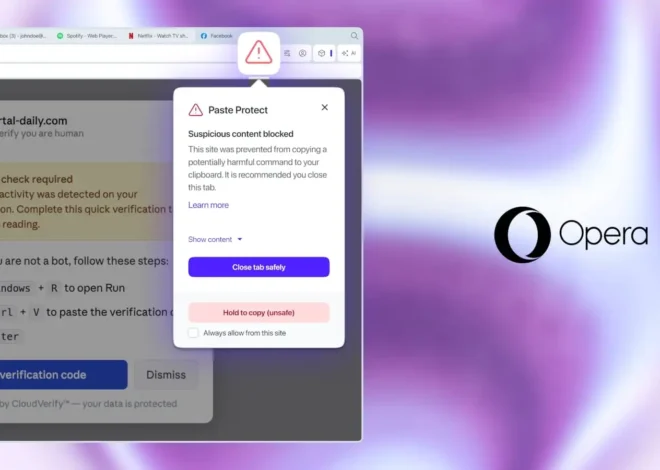
Opera rolls out Paste Protect feature to fight ClickFix attacks
Opera has introduced Paste Protect, a security feature designed to block ClickFix-style attacks that trick users into executing malicious commands through social engineering. ClickFix is a widely used technique where victims are deceived into copying dangerous code or commands to the clipboard and then executing them in the command-line interface. Typically, the ruse is a verification process or some […]
Alleged Scattered Spider hacker extradited to the United States
A dual United States and Estonian citizen has been extradited to the U.S. to face charges alleging he was a member of the Scattered Spider hacking collective. 19-year-old Peter Stokes (who used the online handles “Bouquet,” “Spencer,” and “Jordan”) was arrested in Finland on April 10 while attempting to board a flight to Japan at Helsinki’s […]
Medtronic notifies customers impacted by ShinyHunters data breach
Healthcare device firm Medtronic is notifying affected customers about a data breach that exposed their personal data to an unauthorized third party. The company previously confirmed that its IT systems were compromised by hackers, and the infamous data extortion group ‘ShinyHunters’ claimed the attack. The threat actor said that they were holding 9 million Medtronic records with […]
FortiBleed credential-theft campaign linked to Lynx ransomware
The massive FortiBleed credential theft campaign has been linked to the INC and Lynx ransomware operations, suggesting the stolen Fortinet credentials were intended to fuel future network intrusions. Earlier this month, a server containing credentials stolen from more than 73,000 Fortinet devices was discovered exposed on the internet. Researchers found the server contained downloaded FortiGate […]
Kubota says hackers had month-long access to network systems
Kubota North America Corporation disclosed that hackers had access to some of its network systems for more than a month earlier this year. Following an investigation into the incident, the company determined that between March 16 and April 20 the threat actor accessed files with personal information for employees and their dependents. Kubota is a […]
New ChocoPoC malware targets researchers via trojanized PoC exploits
Multiple weaponized proof-of-concept (PoC) exploits on GitHub were found delivering a Python-based remote access trojan (RAT) named ChocoPoC that can execute commands and steal sensitive data in a campaign believed to target cybersecurity researchers. Hiding malware in PoC exploits for various vulnerabilities is not new, as there are examples of threat actors posing as real security researchers and taking […]
DHS confirms hackers breached HSIN info-sharing platform
The Department of Homeland Security is investigating a cyberattack that compromised the Homeland Security Information Network (HSIN), a sensitive information-sharing platform used by federal, state, local, and private-sector partners. The intrusion, first reported by Nextgov, was carried out by an unknown threat actor in recent weeks and is believed to have occurred sometime between late May […]
Hackers target Microsoft 365 accounts with 81 million login attempts
An aggressive password-spraying campaign targeting Microsoft 365 environments generated more than 81 million login attempts over a two-week period. The threat actor tried to authenticate via Microsoft’s Azure command-line interface (CLI) using still valid username and password combinations that had been exposed in past breaches. Microsoft’s Azure CLI is used for managing Azure cloud resources, […]
Over 900 Oracle E-Business instances exposed to ongoing attacks
Over 900 Oracle E-Business Suite (EBS) instances have been found exposed online amid ongoing attacks exploiting a critical security flaw. The vulnerability (tracked as CVE-2026-46817) was found in the File Transmission component of EBS’s Oracle Payments product and allows malicious actors without privileges and with HTTP network access to take over vulnerable systems through low-complexity attacks. […]
Amazon fined $2.25M for withholding evidence from fraud victims
The U.S. Federal Trade Commission (FTC) says Amazon will pay a $2.25 million civil penalty to settle charges that it blocked identity theft victims’ access to transaction records. As alleged in a complaint filed with the Justice Department, Amazon failed to provide many fraud victims with records of fraudulent transactions made in their names, as […]