ransomware

Qilin ransomware claims Asahi brewery attack, leaks data
The Qilin ransomware group has claimed the attack on Japanese beer giant Asahi by adding the company to the list of victims on its data leak site. The threat actor claims to have exfiltrated more than 9,300 files in 27GB of data. As proof of the theft, the hackers published 29 images showing internal financial documents, employee […]

Hackers now use Velociraptor DFIR tool in ransomware attacks
Threat actors have started to use the Velociraptor digital forensics and incident response (DFIR) tool in attacks that deploy LockBit and Babuk ransomware. Cisco Talos researchers assess with medium confidence that the attacker behind the campaigns is a China-based adversary tracked as Storm-2603. Velociraptor is an open-source DFIR tool created by Mike Cohen. The project has been […]

Microsoft: Critical GoAnywhere bug exploited in ransomware attacks
A cybercrime group, tracked as Storm-1175, has been actively exploiting a maximum severity GoAnywhere MFT vulnerability in Medusa ransomware attacks for nearly a month. Tracked as CVE-2025-10035, this security flaw impacts Fortra’s web-based secure transfer GoAnywhere MFT tool, caused by a deserialization of untrusted data weakness in the License Servlet. This vulnerability can be exploited remotely in low-complexity […]

XWorm malware resurfaces with ransomware module, over 35 plugins
New versions of the XWorm backdoor are being distributed in phishing campaigns after the original developer, XCoder, abandoned the project last year. The latest variants, XWorm 6.0, 6.4, and 6.5, appear to be adopted by multiple threat actors and have support for plugins that allow a wide range of malicious activities. Malware operators can use […]
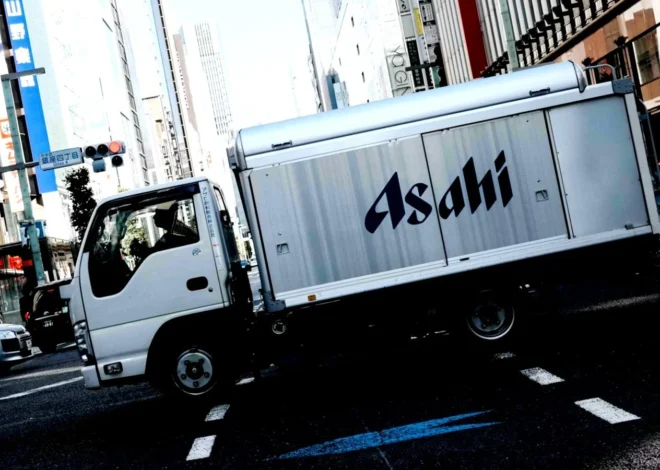
Japanese beer giant Asahi confirms ransomware attack
Japanese beer-making giant Asahi has disclosed today that a ransomware attack caused the IT disruptions that forced it to shut down factories this week. The Tokyo-based beverage holding company is the largest beer brewer in Japan, employing 30,000 people and producing 100 million hectoliters of beverages. The company also owns the Peroni, Pilsner Urquell, Grolsch, […]

Oracle links Clop extortion attacks to July 2025 vulnerabilities
Oracle has linked an ongoing extortion campaign claimed by the Clop ransomware gang to E-Business Suite (EBS) vulnerabilities that were patched in July 2025. While the company has yet to attribute the attack to this ransomware operation, Rob Duhart, the Chief Security Officer of Oracle, confirmed that customers had received extortion emails from the gang. Duhart also […]

Clop extortion emails claim theft of Oracle E-Business Suite data
Mandiant and Google are tracking a new extortion campaign where executives at multiple companies received emails claiming that sensitive data was stolen from their Oracle E-Business Suite systems According to Genevieve Stark, Head of Cybercrime and Information Operations Intelligence Analysis at GTIG, the campaign began in late September. “This activity began on or before September […]

Data breach at dealership software provider impacts 766k clients
A ransomware attack at Motility Software Solutions, a provider of dealer management software (DMS), has exposed the sensitive data of 766,000 customers. Motility (formerly known as Systems 2000/Sys2K) is a provider of DMS software used by 7,000 dealerships (automotive, powersports, marine, heavy-duty, and RV retail) across the United States. Its products cover customer relationship management (CRM), […]

Google Drive for desktop gets AI-powered ransomware detection
Google has begun rolling out a new AI-powered security feature for Google Drive desktop, which will automatically pause file syncing when it detects a ransomware attack to minimize impact. While this will not block ransomware from encrypting files on the infected computer, users’ documents stored in Google Drive will be protected and can be easily […]

Ransomware gang sought BBC reporter’s help in hacking media giant
Threat actors claiming to represent the Medusa ransomware gang tempted a BBC correspondent to become an insider threat by offering a significant amount of money. Cybersecurity correspondent Joe Tidy revealed in a story on the BBC that the hackers wanted to use his laptop to breach the British public-service broadcaster’s network and then ask for a ransom. […]